Help & Documentation>TDMQ for CKafka>Operation Guide>Obtaining Access Permission>Grant operational-level permissions to sub-accounts

Grant operational-level permissions to sub-accounts

Last updated: 2023-09-07 16:07:26

Scenario

This document guides you through using a Tencent Cloud root account to grant operational-level permissions to sub-accounts. You can grant different read and write permissions to sub-accounts based on your actual needs.

Instructions

Grant full read and write permissions

Note
After granting full read and write permissions to a sub-account, the sub-account will have complete read and write capabilities for all resources under the root account.
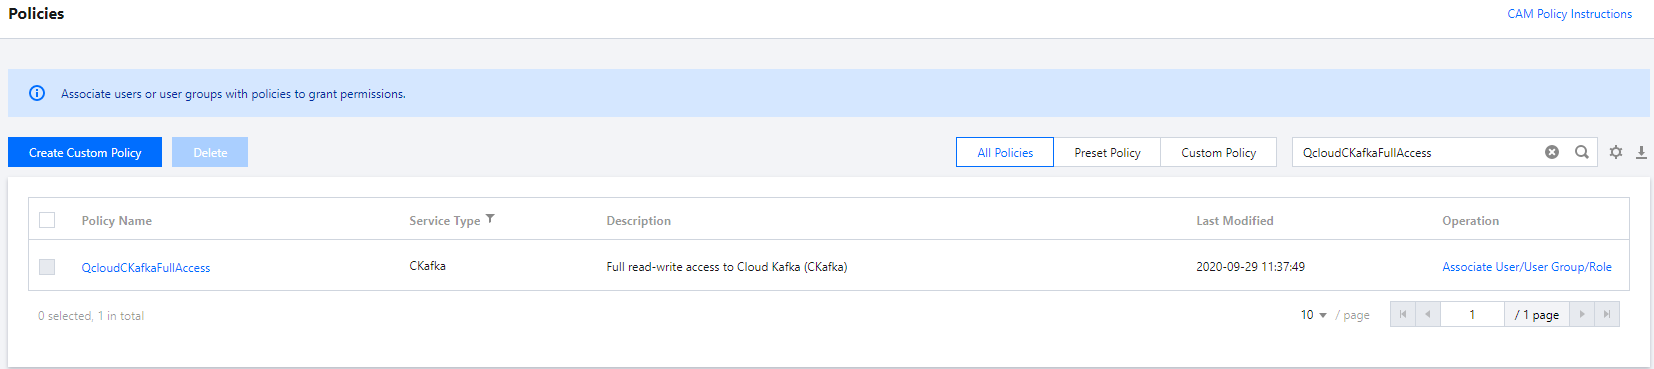
1. Log in to the CAM console as the root account.
2. In the left sidebar, click Policies to go to the policy management page.
3. Search for QcloudCKafkaFullAccess in the search bar on the right.


4. In the search results, click the Associated Users/Groups of QcloudCKafkaFullAccess and select the sub-account to be authorized.


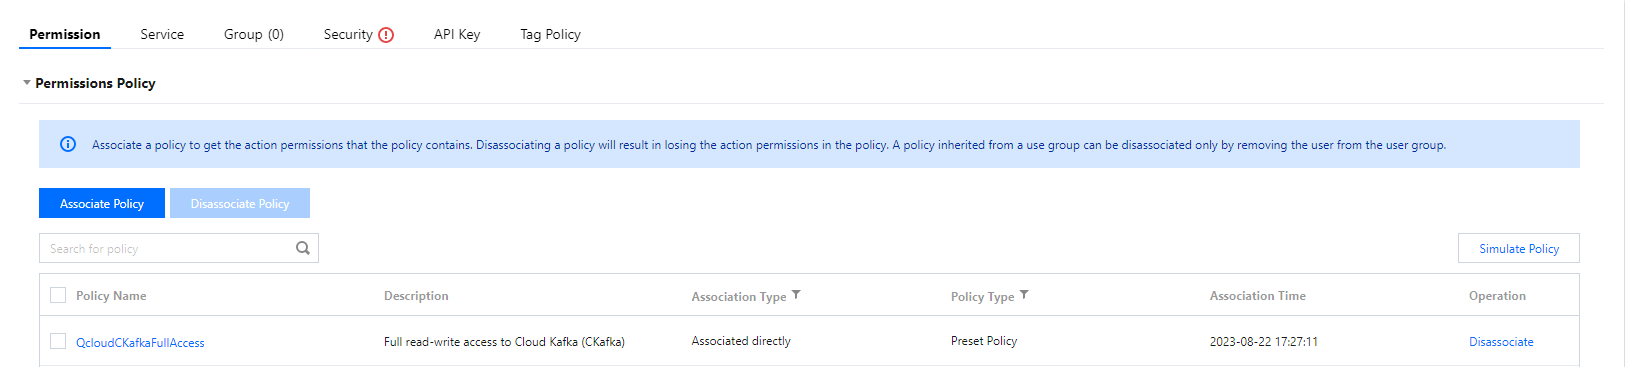
5. Click OK to complete the authorization. The policy will be displayed in the user's policy list.


Grant read-only permissions

Note
After granting read-only permission to a sub-account, the sub-account will have read-only access to all resources under the root account.
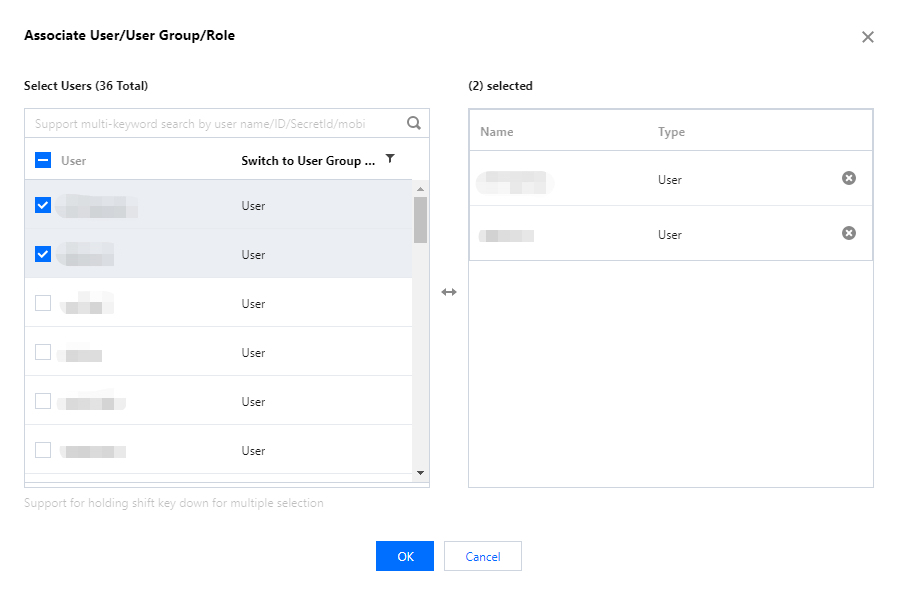
1. Log in to the CAM console as the root account.
2. In the left sidebar, click Policies to go to the policy management page.
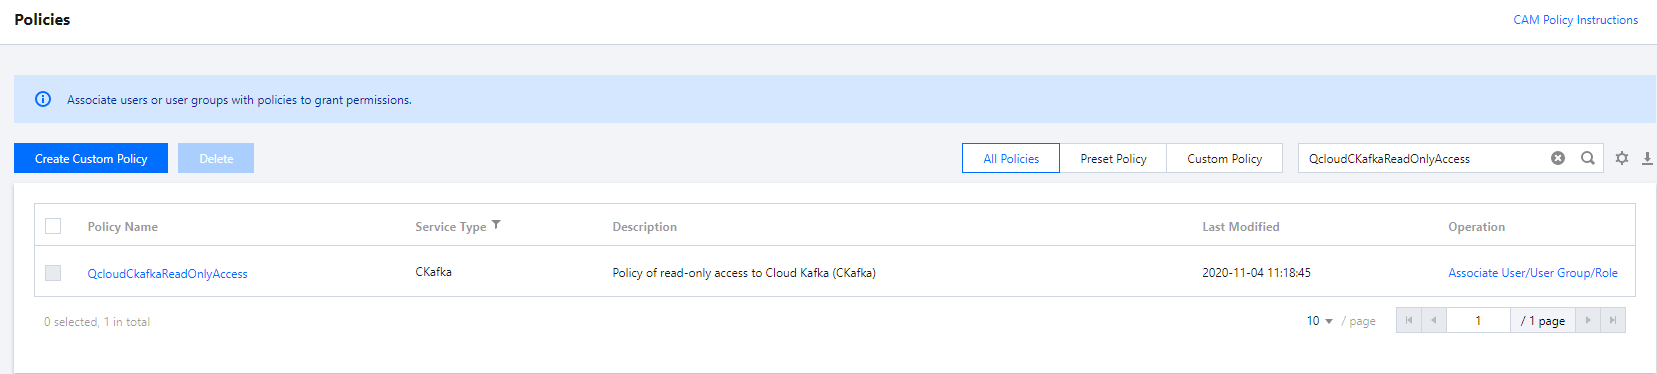
3. Search for QcloudCKafkaReadOnlyAccess in the right search bar.


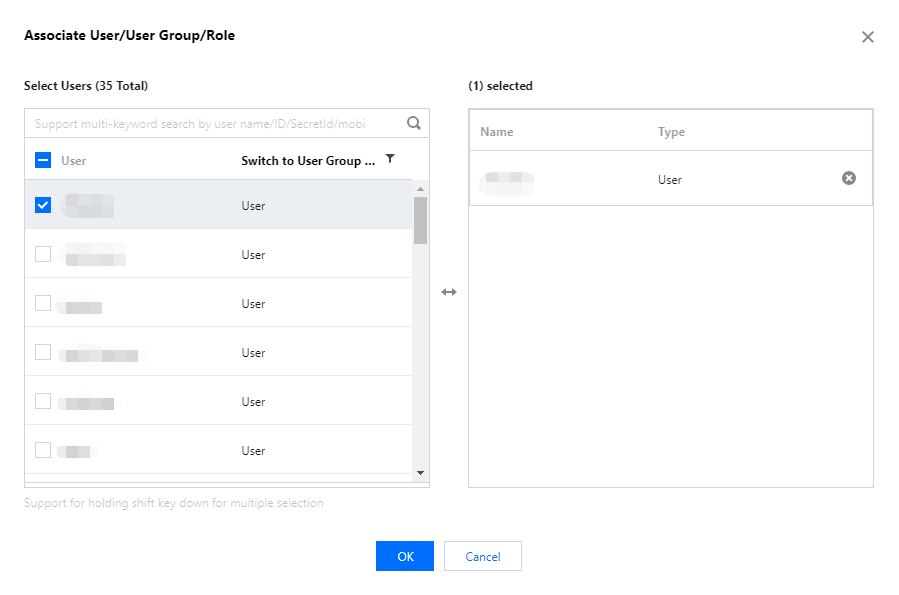
4. In the search results, click the Associated Users/Groups of QcloudCKafkaReadOnlyAccess and select the sub-account to be authorized.


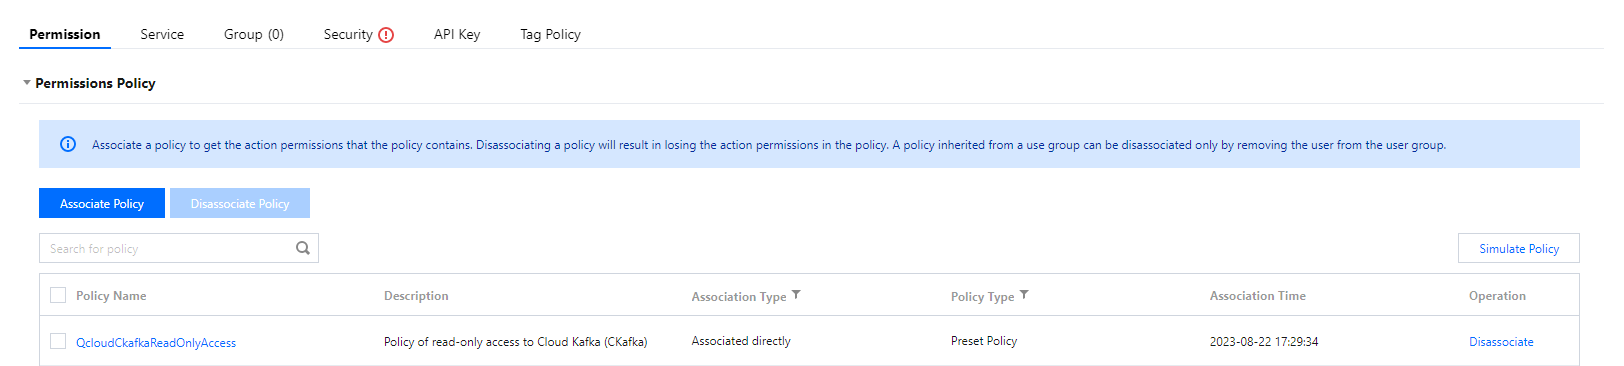
5. Click OK to complete the authorization. The policy will be displayed in the user's policy list.


Other authorization methods