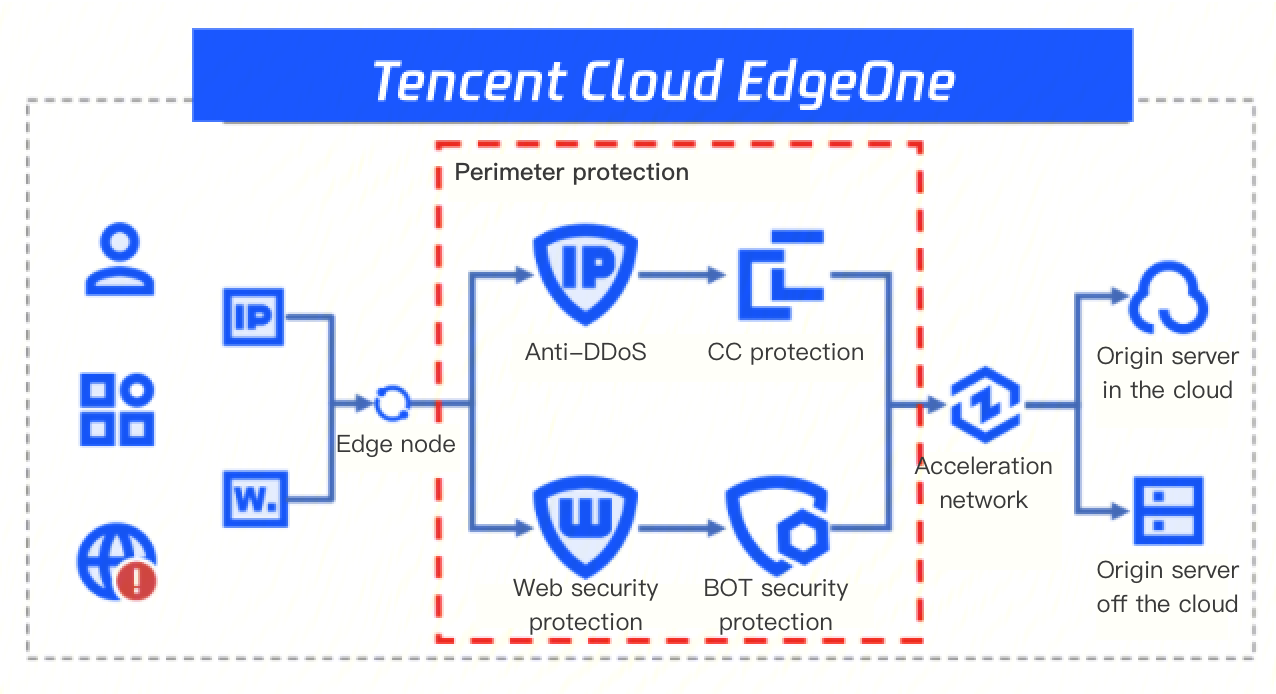
EdgeOne is an integrated edge security and acceleration platform offering 3D protection from layers 3 to 7.
Anti-DDoS: It detects and cleanses DDoS attack traffic and guarantees the business availability based on diverse measures, for example, IP blocklist/allowlist and port blocking policies.
Rate limit: It uses mechanisms such as HTTP field match and access frequency monitoring to effectively cleanse CC attack traffic.
Web security protection: It effectively prevents top 10 OWASP web ricks like SQL injection and cross-site scripting (XSS) and quickly identifies and blocks bot behaviors.
API security protection: It guarantees API access security based on a secure and reliable access authentication mechanism.
Web or Bot Attack Protection
Bot recognition and protection
Based on the characteristics of protocols, IP intelligence, and custom sessions, it can accurately recognize and block various bots. In addition, it leverages data and threat intelligence to comprehensively analyze and learn crawler behaviors to build a crawler recognition model, which effectively solves problems of malicious crawler passthrough and benign crawler kill.
Web attack protection
With a rich attack signature library covering common OWASP security threats, it effectively blocks web attacks, exploits, trojans, backdoors, and other web service security issues, and provides zero-day vulnerability defense. Leveraging a syntax analysis and AI-based intelligent detection engine, it enhances detection accuracy and effectively reduces false positives.
Around-the-clock active monitoring and response
Tencent Security team monitors your business security 24/7 to discover and respond to problems actively, greatly improving the responsiveness.
Smart Protection
A smarter automatic protection service is developed based on multiple years of experience in attack backtracking.
Smart captcha
Leveraging years of experience in combating CC attacks and research on the latest trends in CC protection, we have developed an effective system for marking and identifying clients. By continuously tracking clients, we effectively resolve issues of attack penetration and false positives in high-intensity attack scenarios.
Automatic API recognition
Through deep analysis based on big data and feature comparison across multiple dimensions such as UA, root directory, and CGI, an accurate API auto-identification model is constructed. This model automatically identifies API interfaces, avoids false positives, and significantly enhances API protection capabilities.
Attack tracing
As an important component in response during and after security events, attack backtracking analyzes and collects evidence from the attack traffic to reveal the attack means used by attackers and get important information like attack source IPs and attack methods. This helps with subsequent protection policy adjustment and attack source tracing to avoid secondary attacks.
The system conducts packet capture analysis on abnormal/attack events, extracting the attack source and attack messages, which can serve as crucial evidence for attack tracing. Simultaneously, the EdgeOne platform provides a comprehensive monitoring page, displaying various information such as attack types, attack sources, attack ports, and attack traffic, providing a basis for users to adjust their protection strategies.
Accurate Attack Source Positioning
Fingerprint identification solution: It accurately locates the source of the attack, ensuring that normal business operations remain unaffected.
Protocol flood attack protection
Attackers launch attacks by randomly forging a large amount of traffic from uncommon protocols. The system, based on basic protection strategies such as protocol interception, regional traffic interception, blocklists/allowlists, and network ACLs, and our proprietary fingerprint recognition solution, deeply identifies and matches each feature field of the protocol, cleanses all types of protocol flood attack traffic, and ensures that normal business operations are not affected.
Accurate attack source positioning through fingerprint algorithm
Based on passive analysis of massive amounts of traffic and characteristics of multiple parameters such as TCP option, timestamp, and TTL, EdgeOne automatically determines the client operating system, application type, and device UID to accurately recognize attack sources. This helps effectively tackle different industry challenges like CC attack protection passthrough.